ACE: one score, one action list, every client
The AI layer over every Control Hub service. ACE correlates signals across network, assets, threats, exposure and AI use, helps you prioritize what needs attention, and recommends or carries out a response through the relevant control, depending on the action.
Stop Chasing Alerts, Start Closing Risks
One laptop can show up in every tool, each with a different severity. Your team sorts noise instead of fixing problems, and your client never sees the value you deliver. ACE correlates signals across endpoint, email, identity, dark web, device management, exposure and AI use into one prioritized action list per client: cross-control correlation, not more alerts. Fewer alerts and faster answers, for the business being protected and the MSP protecting it.
One real client environment, anonymized.
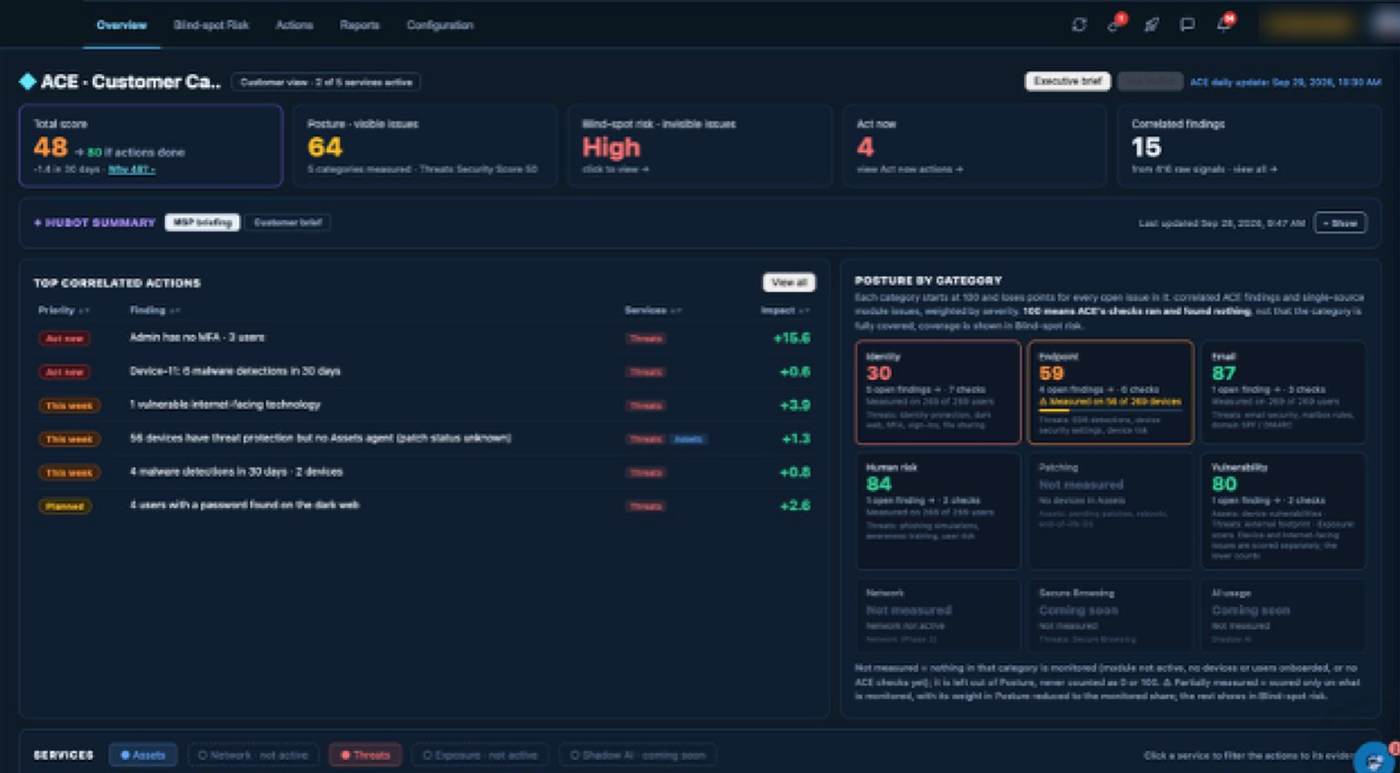
Customer Security Dashboard
One score that tells the whole story.
See each customer’s security on one screen: a single Total Score, what’s exposed, and what you can’t see yet. ACE turns 45 raw signals into 7 prioritized actions and shows how many points each one is worth.
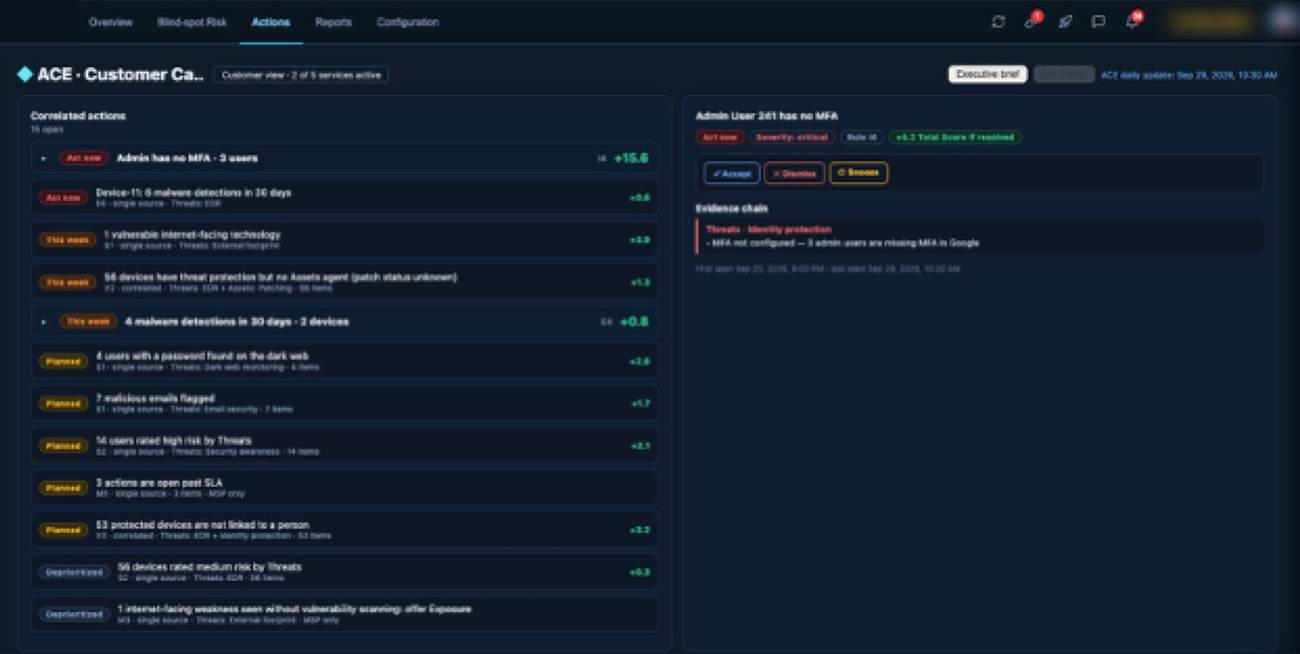
Correlated Actions
From noise to a to-do list.
ACE connects findings across your security and RMM tools, so you work on root causes instead of duplicate alerts. Each action names the exact devices involved, and you can accept, dismiss or snooze it in one click.
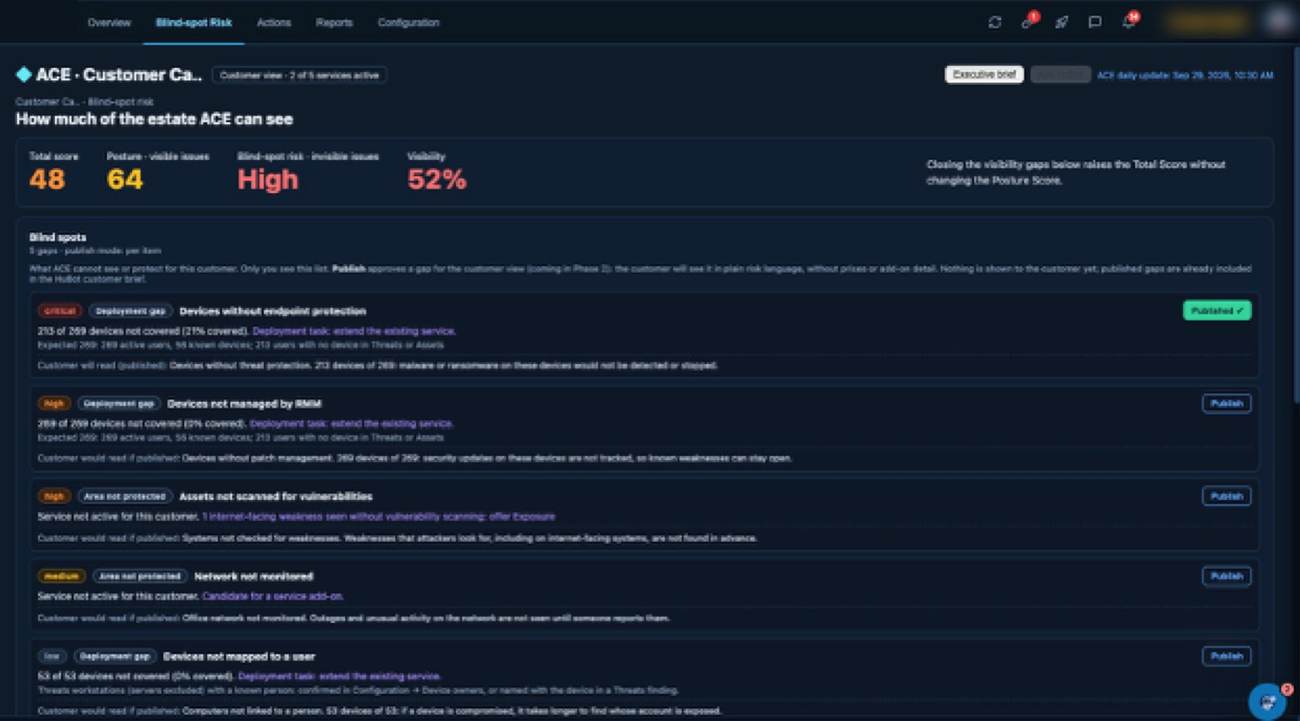
Blind-spot Risk
Know what you can’t see.
A security score is only as good as its coverage. ACE shows which devices and users fall outside your protection, how much each gap costs in score, and the specific step that closes it, written in plain language your customer can understand.
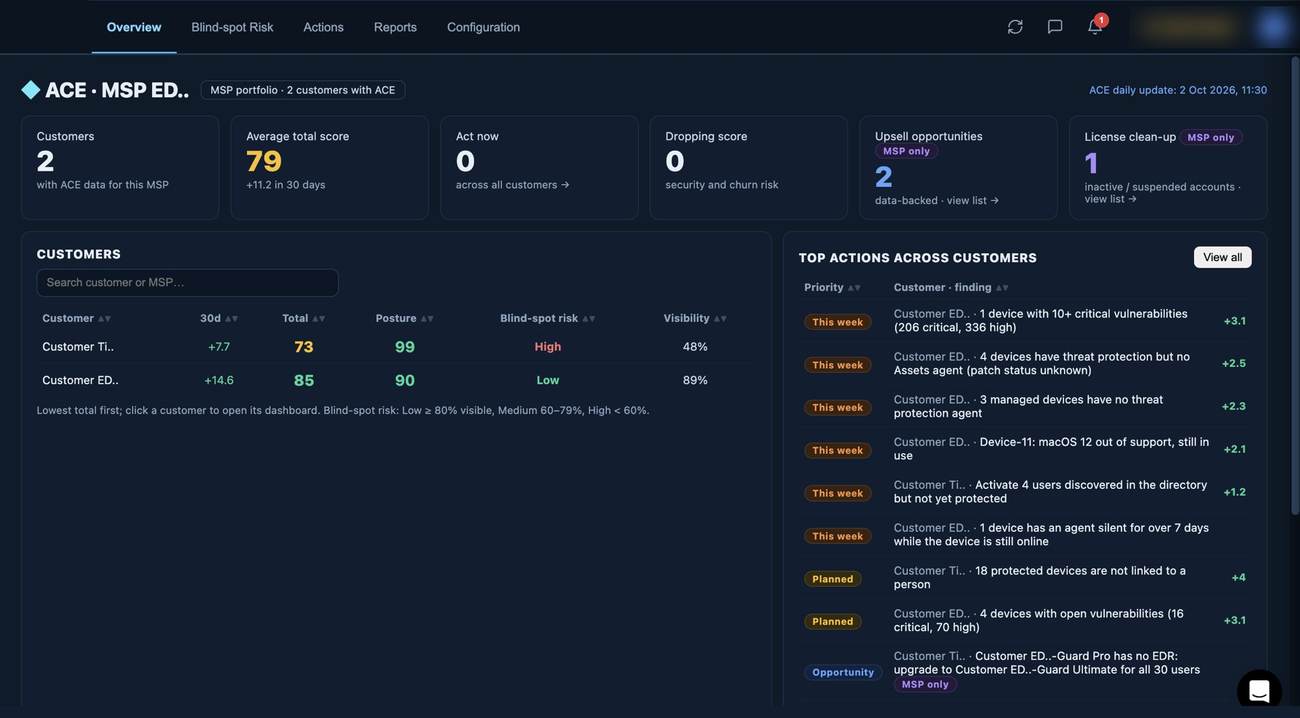
MSP Portfolio Overview
Your whole customer base, ranked by risk.
Spot falling scores before a customer churns, and see the most important actions across every tenant in one list. Upsell and license clean-up opportunities come from each customer’s own data and are visible only to you.
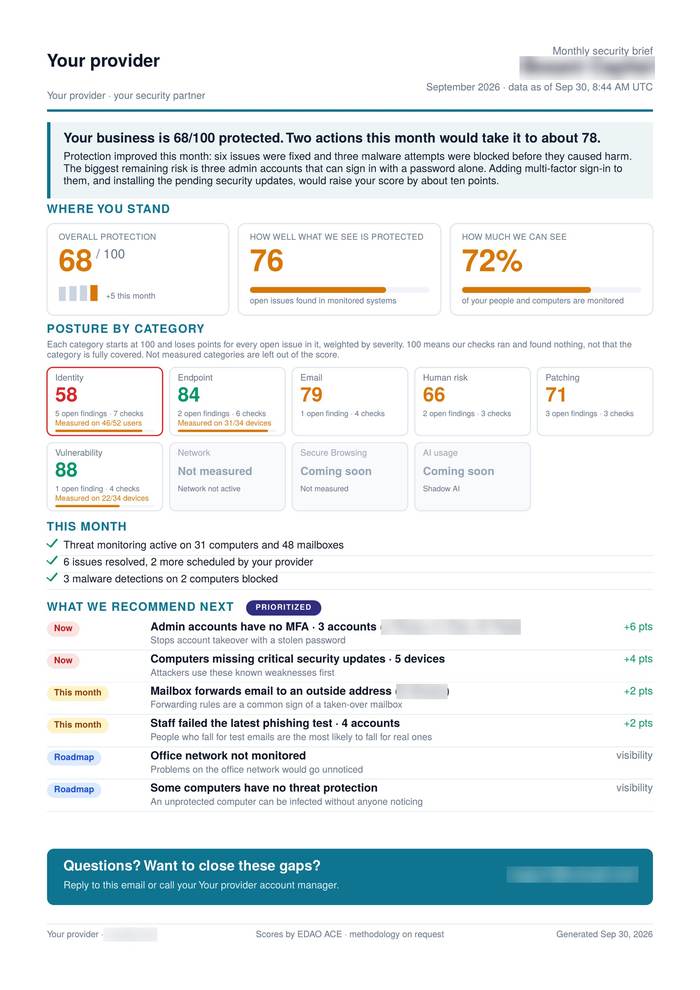
Monthly Executive Brief
Security your customers can actually read.
A white-labeled brief under your brand: one score, what changed, and what to fix next. No jargon, no dashboards.
Where you stand
One clear score, with every recommended action showing the points it adds.
At a glance
Actively exploited risks with their exact fixes, plus the blind spots worth closing.
ACE in action
The same first signal can end in a report or in containment. What changes the outcome is what ACE knows about the same device, user or client from the other services.
Exposed service under attack
- MidRemote access port open to the internetRecommend: restrict to VPN or close it
- High+ an exploitable vulnerability on that serviceEnforce: patch or disable the service until patched
- Critical+ repeated failed logins from outsideContain: block the source IPs, disable the service, check for a successful login
ACE connects: an exposed remote access service, a vulnerability and failed logins, giving you context to review the risk together.
Refused patch, then malware
- LowCritical OS patch missingReport: added to the patch queue
- Mid+ the user cancelled or deferred the installEnforce: forced install window, user and admin notified
- High+ malware detected on the same deviceContain: isolate the device, patch after containment, open an incident
ACE connects: patch status and malware detection live in different tools; ACE joins them on one device.
One flaw, many clients
- LowCritical vulnerability on devices at one clientHandled inside that client
- Mid+ the same vulnerability across many of your clientsEnforce: one patch campaign across every affected client
- High+ an exploit attempt at one of themContain: the campaign jumps the queue; mitigation on clients not yet patched
ACE connects: the same vulnerability across clients, so you can review the affected devices and plan a coordinated response.
Stolen account driving an AI agent
- LowEmployee credential found on the dark webRecommend: ask the user to change the password
- Mid+ the same user works through an AI agentEnforce: password reset, MFA enrollment, review what the agent can reach
- High+ suspicious login on that accountContain: revoke sessions, suspend the agent, block the account
ACE connects: a leaked credential, the user’s AI agent access and a suspicious login, so you can review the account and the agent’s permissions together.
Answers you can defend
Deterministic
ACE uses AI to correlate signals, and its results are deterministic: the same data always gives the same result.
Traceable
Every finding traces straight back to its source service and evidence.
Always fresh
ACE runs daily for every client, and within minutes when a critical event occurs.
See ACE live
A demo with your own client scenarios.