EDAO VEM
Fix the weaknesses that matter most, not just the next item on a scan. See vulnerabilities by severity, compare risk across clients and understand exposure across devices, web apps, cloud, OT and identities—so your team can prioritize remediation where it matters.
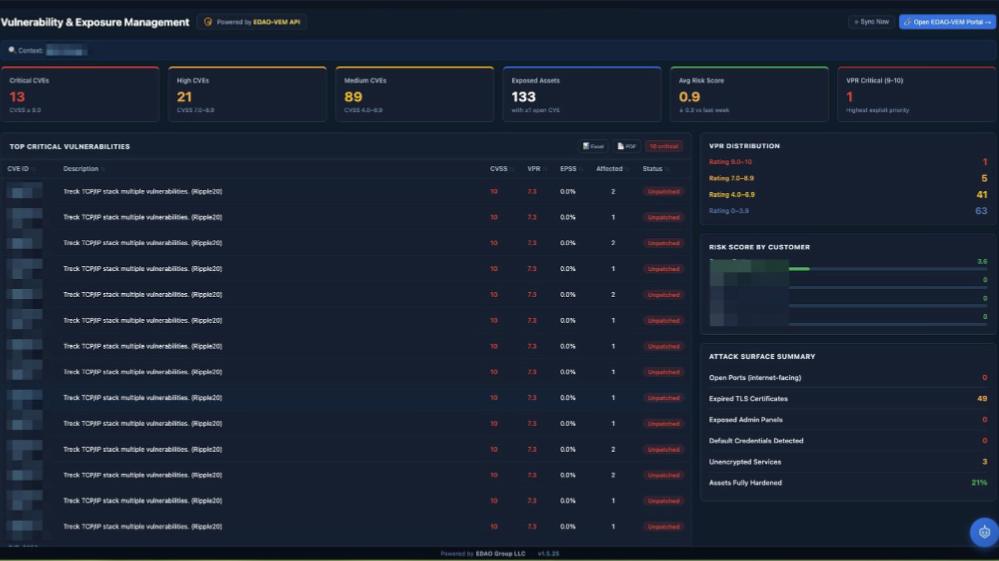
EDAO VEM in Control Hub: vulnerabilities by severity, risk by client and the attack surface summary.
What’s included
Vulnerability management
Find and track vulnerabilities across your clients’ devices and servers.
Web app scanning
Scan web applications for security weaknesses.
Cloud security
Check cloud environments for exposures and misconfigurations.
Operational technology (OT)
Extend vulnerability visibility to OT environments.
Attack surface management
See what is exposed to the internet, from open ports to expired certificates.
Attack path analysis
Understand how an attacker could move from one weakness to the next.
Identity exposure
Spot identity weaknesses, such as Active Directory misconfigurations.
From scattered findings to clear priorities
Exposure view
Aggregated cyber risk insights.
Attack path analysis
Breach and attack mitigation.
Asset inventory
A centralized view of assets.
Exposure analytics
Data aggregation, risk prioritization and recommendations, and benchmarking.
The vulnerability management lifecycle
A continuous cycle, not a one-off scan: every fix is verified, and every new finding starts the loop again.
Discover
Find every asset and its vulnerabilities across devices, web apps, cloud, OT and identities.
Prioritize assets
Rank assets by how important they are to the business.
Assess
Score each vulnerability by severity and how likely it is to be exploited.
Report
Turn findings into clear reports for your team and your clients.
Remediate
Fix the issues that matter most first.
Verify
Rescan to confirm each fix worked, then start the next cycle.
Protect your clients with EDAO VEM
Part of the EDAO Control Hub, and correlated by ACE.